Virtual
AI adoption is moving faster than many organizations' governance, security and compliance programs can keep up.
As businesses introduce AI into products, operations and decision-making, customers, regulators, insurers and enterprise partners are beginning to ask harder questions about how AI systems are governed, what data they use, how risks are managed and whether existing security controls are still sufficient.
This practical workshop will help business and technology leaders understand what is changing and how to prepare. We will explore emerging AI governance expectations through the lens of SOC 2, the NIST AI Risk Management Framework and Canadian privacy considerations including PIPEDA and PHIPA and translate them into practical actions organizations can take now.
The session is designed to give attendees a practical starting point for responsible AI adoption without slowing innovation.
- Where AI creates new governance, security and compliance exposure
- What customers, regulators and insurers are increasingly likely to ask
- How existing cybersecurity and compliance programs can be extended to cover AI risk
- Practical steps organizations can take now to assess gaps and strengthen AI readiness
Business and technology leaders responsible for AI adoption, cybersecurity, risk, privacy and compliance, including:
- C-suite executives and business owners
- CIOs, CTOs and CISOs
- IT and security leaders
- Compliance, risk and privacy leaders
- Product and technology leaders
Priority organizations:
- Technology and SaaS
- Financial services
- Healthcare and healthtech
- Other regulated or data-intensive businesses
Darace Rose is CEO and Co-Founder of Oppos Incorporated, a Toronto-based cybersecurity and compliance company. Darace helps businesses, from growing teams to large regulated organizations, answer the questions customers, regulators and insurers are now asking about AI, whether they're building on the security and privacy programs they already have or establishing compliance for the first time. Oppos's RegAI platform supports SOC 2, ISO 27001, ISO 42001, the NIST AI RMF, PIPEDA and PHIPA. A Canadian-Jamaican founder and Board of Trade member, Darace also advises underrepresented entrepreneurs on compliance, fundraising and building lasting businesses.
Dr. Mehdi Karimi is a cybersecurity leader with 25 years of experience helping organizations turn security and compliance into a business advantage. He has been a seasoned CISO for multiple SaaSy and cloud-front organizations both in USA and Canada. Mehdi leads the company’s ISO 27001 and SOC 2 programs. He leads the AI governance model - the ISO 42001 advisory board. Mehdi serves as a fractional CISO to highly regulated environments in technology, space, insurance and financial services. His forte spans FedRAMP 20x, CMMC, ITSP 10.171, NIST 800-53, GDPR, PCI-DSS, SOC 2 and ISO standards, with a focus on migrating existing control frameworks to emerged AI without slowing innovation. Mehdi holds a PhD in Electrical and Computer Engineering from the University of British Columbia, specializing in cybersecurity. He is also the inventor on 2 AI patents. His peer-reviewed research in leading IEEE and ACM venues, including a Best Paper Award at DSN'21, has been cited more than 350 times.
Agenda
12:00 – 12:05 | Welcome and Opening Remarks
Toronto Region Board of Trade
12:05 – 12:15 | The AI Governance Gap: Where the New Exposure Is
How AI in products, operations and decision-making creates new governance, security and compliance risk: shadow AI, sensitive data in prompts, third-party AI vendors and automated decisions.
- Darace Rose, CEO & Co-Founder, Oppos Incorporated
12:15 – 12:25 | What Customers, Regulators and Insurers Will Ask Next
The questions now showing up in security reviews, enterprise contracts, cyber insurance renewals and privacy obligations under PIPEDA and PHIPA, and what a credible answer looks like.
- Darace Rose
12:25 – 12:40 | Extending Your Existing Programs to Cover AI
Building on what you already have instead of starting over:
- Mapping SOC 2 controls to AI risk
- Using the NIST AI Risk Management Framework (Govern, Map, Measure, Manage) as a practical structure
- Keeping humans in the loop: review, approval and evidence for AI outputs
- A brief walkthrough of how this looks in practice
Mehdi Karimi, Cybersecurity Consultant, Oppos Incorporated
12:40 – 12:50 | Your 90-Day AI Readiness Plan
Practical steps you can start now: inventory your AI use, assign ownership, set an acceptable-use policy, assess vendors, close priority gaps and collect evidence before anyone asks for it.
- Mehdi Karimi
12:50 – 1:00 | Live Q&A and Closing
Audience questions, key takeaways and next steps, including how to access a complimentary AI readiness assessment.
- Darace Rose and Mehdi Karimi
Speakers
-
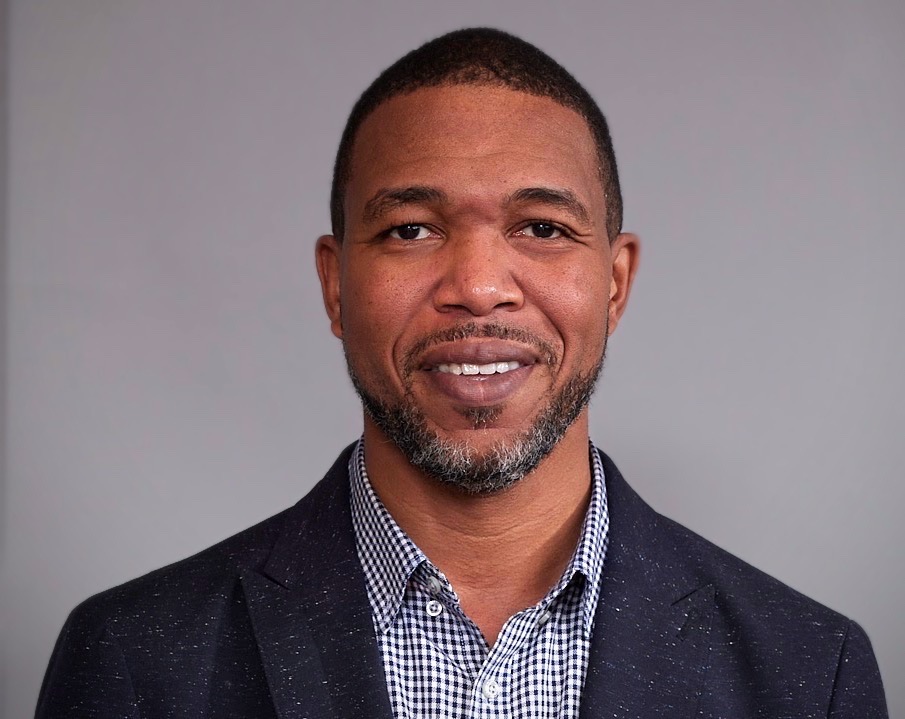
Darace Rose
Founder & CEO
Oppos Inc
-
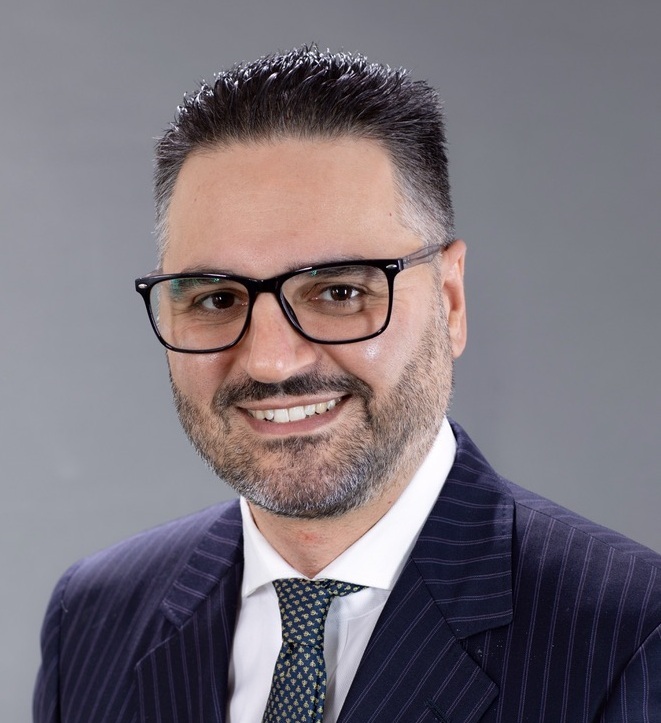
Dr. Mehdi Karimi
Cybersecurity expert
Tickets & Registration
This event is free.